All Categories
Featured

The Role of Generative Models in Engineering New Solutions
Table of Contents
- – The Transition to Decentralized Research Study...
- – Advanced Encryption and Data Partition Techniques
- – Hardware Security and the Role of Secure Enclaves
- – AI-Driven Danger Intelligence and Behavioral A...
- – Regulatory Compliance and Data Sovereignty
- – Constructing a Culture of Security in Research...
The Transition to Decentralized Research Study Environments in 2026
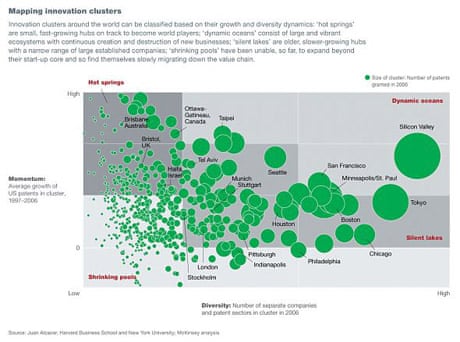
The centralized laboratory model has actually mainly faded into the past by 2026. High-performance development centers now operate as decentralized networks of specialized nodes, permitting organizations to tap into global skill pools without the restraints of a single physical head office. While this shift has actually sped up the speed of discovery, it has also presented substantial security vulnerabilities. Safeguarding proprietary data across these distributed networks requires a shift in how engineers and security architects view the boundary. In 2026, the concept of a "safe" internal network no longer exists. Every connection, whether it originates from a home office in a rural district or a modern satellite center, is treated with equivalent suspicion.
The technical architecture of these networks relies on a No Trust architecture where identity acts as the primary security boundary. Organizations are moving away from standard passwords in favor of constant authentication procedures. These systems analyze behavioral patterns, such as typing rhythm, cursor motion, and even biometric telemetry gathered from wearable devices, to confirm that the individual accessing the R&D database is certainly who they declare to be. This level of examination happens in the background, minimizing the friction that frequently slows down imaginative work. When these protocols recognize a deviation from the established baseline, gain access to is immediately withdrawed or limited to low-level information till more confirmation is provided.
Security teams in 2026 focus greatly on the stability of the hardware itself. Distributed R&D indicates that physical control over every endpoint is impossible. To counter this, business have actually embraced silicon-based root-of-trust mechanisms. These microchips are embedded at the production stage and supply a protected structure for every other layer of the software stack. If the hardware is tampered with or if the firmware is replaced by an unauthorized party, the device becomes incapable of decrypting the network's information. This avoids taken or compromised hardware from ending up being an entry point for corporate espionage.
Advanced Encryption and Data Partition Techniques
The mathematics of information protection has actually altered substantially in 2026 with the arrival of quantum-resistant algorithms. As quantum computing abilities have broadened, the encryption methods that once seemed solid are now thought about high-risk. Research networks must shift to lattice-based cryptography and other post-quantum requirements to ensure that information caught today stays protected against the decryption abilities of tomorrow. This is particularly important for R&D projects with long lifecycles, such as pharmaceutical development or aerospace engineering, where the copyright needs to remain confidential for decades.
Preserving high efficiency while guaranteeing security is a delicate balance. One method companies achieve this is through homomorphic encryption. This innovation allows scientists to carry out calculations on encrypted data without ever having to decrypt it. A data scientist can run an analysis on a sensitive dataset while the raw information remains concealed, even from the researcher. This significantly minimizes the threat of information leaks throughout the analysis phase. Carrying out Robust Enterprise Innovation Models throughout these workflows makes sure that collective projects can continue without researchers needing to see the full breadth of the underlying proprietary sets.
Data partition stays an important element of these security procedures. By micro-segmenting the network, architects can isolate specific research projects from one another. A breach in a products science department does not always lead to a compromise in the propulsion laboratory. These sectors are often ephemeral, created for the duration of a particular job and after that liquified as soon as the work is total. This lowers the time a risk star needs to move laterally through the network if they handle to discover a point of entry. The objective is to reduce the "blast radius" of any prospective security occasion.
Hardware Security and the Role of Secure Enclaves
Safe and secure enclaves have actually ended up being standard in 2026 for any top-level R&D task. These are isolated areas within a processor that are different from the main os. Even if the whole computer is jeopardized by malware, the information kept and processed within the protected enclave stays protected. Researchers utilize these enclaves to handle the most delicate aspects of their work, such as secret keys or proprietary algorithms. The seclusion is implemented at the hardware level, making it almost impossible for unapproved software application to peek into the enclave's memory.
The reliance on Enterprise Innovation within the broader technology stack has actually grown as the requirement for specialized computing boosts. Distributed networks often use heterogeneous computing, blending CPUs, GPUs, and specialized AI accelerators. Each of these parts should have a validated security posture before it is enabled to sign up with the research study network. Automated scanning tools examine the setup and patch levels of these devices in real-time. If a device fails to fulfill the necessary security requirement, it is immediately quarantined from the remainder of the node till it is restored into compliance.
Physical security at remote nodes is managed through a mix of automated security and geo-fencing. Access to R&D data is frequently limited to particular geographic coordinates. If a researcher tries to log in from an unapproved location, the system can block the request or need additional layers of authentication. In 2026, numerous companies likewise utilize tamper-evident storage for their local caches. If the physical housing of a storage system is opened or customized, the internal drives trigger an instant wipe of all cryptographic secrets, rendering the data useless.
AI-Driven Danger Intelligence and Behavioral Analysis
Expert system is both a tool for opponents and a main defense for R&D networks. By 2026, security operations centers rely greatly on AI to process the massive volume of logs created by dispersed systems. These AI models are trained to recognize the subtle signs of a targeted attack, such as a slow and methodical exfiltration of small data packages that may go unnoticed by human screens. The systems try to find anomalies in information gain access to patterns, such as a scientist all of a sudden downloading large volumes of files unrelated to their present project or visiting at unusual hours from a brand-new gadget.
The human component remains a primary issue, as social engineering techniques have become more sophisticated with using generative AI. Attackers can now create highly persuading deepfake audio and video to impersonate executives or task leads. To combat this, research networks have established rigorous procedures for out-of-band verification. Any ask for delicate information or a change in security settings must be confirmed through a separate, pre-verified channel. Training for staff has also evolved to consist of simulations of these innovative AI-driven phishing attempts, keeping the team conscious of the newest methods used by commercial spies.
Automated red teaming is another strategy acquiring traction in 2026. Security systems continually introduce controlled "attacks" by themselves network to discover weaknesses before a real adversary does. This proactive technique enables teams to determine misconfigured cloud pails, unpatched software application, or weak identity controls in real-time. The outcomes of these tests are used to fine-tune the AI defensive designs, creating a feedback loop that continuously enhances the network's resilience. This makes sure that the defense evolves simply as rapidly as the hazards it faces.
Regulatory Compliance and Data Sovereignty
Navigating the complicated world of data sovereignty is a significant obstacle for dispersed R&D. Different regions have varying laws concerning how data is handled, kept, and shared. By 2026, many countries have actually updated their personal privacy policies to represent sophisticated AI and dispersed computing. Organizations should ensure that their security protocols are certified with the laws of every jurisdiction where they have an existence. This often needs storing information within the borders of a particular nation while still allowing researchers in other parts of the world to deal with it through safe and secure, remote user interfaces.
Modern compliance tools are integrated straight into the R&D workflow. As data is created, it is instantly tagged with metadata that specifies its level of sensitivity and the guidelines that apply to it. This metadata follows the information as it moves through the network, guaranteeing that security policies are consistently applied. A dataset subject to strict European personal privacy laws will automatically be limited from being sent to a server in an area with weaker protections. This automatic governance decreases the threat of unexpected non-compliance, which can cause heavy fines and damage to the organization's credibility.
Openness and auditability are also vital. Dispersed networks maintain immutable logs of all information gain access to and modifications, frequently using distributed ledger innovation to make sure the logs can not be tampered with. These logs offer a clear trail of who accessed what info and when, which is important for both regulative audits and internal examinations. In case of a suspected IP leakage, these records permit the security group to trace the source of the breach with high accuracy, identifying exactly which node or account was involved.
Constructing a Culture of Security in Research Clusters
Technology alone can not protect a dispersed R&D network. The culture of the company must also prioritize security. In 2026, scientists are seen as partners in the security process instead of simply users of the system. Security procedures are created to be as unobtrusive as possible, but they require the active participation of every employee. This consists of things like practicing great "digital health," being doubtful of unsolicited interactions, and promptly reporting any suspicious activity. A well-informed workforce is often the very first line of defense against an intrusion.
Cooperation between the security team and the R&D departments is vital. Security architects need to comprehend the workflows of the scientists to construct systems that support, rather than hinder, their work. Regular feedback sessions allow scientists to report pain points where security steps are decreasing their progress. The security group can then discover ways to enhance those procedures or supply alternative tools that fulfill the very same safety requirements. This collective approach makes sure that security is viewed as an enabler of discovery instead of a barrier to it.
As the year 2026 continues to see fast shifts in innovation, the methods for securing distributed research networks will keep evolving. The focus will remain on structure systems that are resistant, versatile, and capable of protecting the world's most valuable intellectual property. By combining hardware-based trust, advanced encryption, and AI-driven tracking, companies can maintain the high-performance environments needed for the next generation of advancements while keeping their essential possessions safe from the ever-changing risk of cyber-attacks.
The decentralization of innovation has actually shown to be an effective design for contemporary organizations. While it brings new challenges, the capability to combine the very best minds from throughout the globe is a powerful benefit. With the right security procedures in location, these distributed networks will continue to be the engines of progress for several years to come. Maintaining the stability of these systems is not simply a technical task, however a tactical need for any company wanting to lead in their particular field.

Table of Contents
- – The Transition to Decentralized Research Study...
- – Advanced Encryption and Data Partition Techniques
- – Hardware Security and the Role of Secure Enclaves
- – AI-Driven Danger Intelligence and Behavioral A...
- – Regulatory Compliance and Data Sovereignty
- – Constructing a Culture of Security in Research...
Latest Posts
The Role of Generative Models in Engineering New Solutions
Managing Large Datasets in AI-Driven R&D Environments
Managing Intellectual Property Within Shared Research Ecosystems
Latest Posts
The Role of Generative Models in Engineering New Solutions
Managing Large Datasets in AI-Driven R&D Environments
Managing Intellectual Property Within Shared Research Ecosystems